Google’s elite security research team has just rewritten the rules that decide when the world learns about a software vulnerability — and the reason is artificial intelligence. On November 13, 2026, Google Project Zero announced a new disclosure policy that will publish the technical details of a bug just 30 days after the vendor is told about it, down from a maximum of 120 days today. For anyone who uses a phone, a laptop, or the cloud, that countdown now matters more than ever.
Project Zero is the team Google tasks with hunting for serious security flaws in other companies’ software — from Microsoft Windows and Apple iOS to browsers and open-source libraries. Its disclosure clock has long been one of the most influential deadlines in cybersecurity: vendors know that if they do not fix a bug in time, Project Zero will publish it anyway. Now that clock is getting dramatically shorter, because AI has changed how fast attackers can work.
What exactly changed: from “90 + 30” to “Full X”
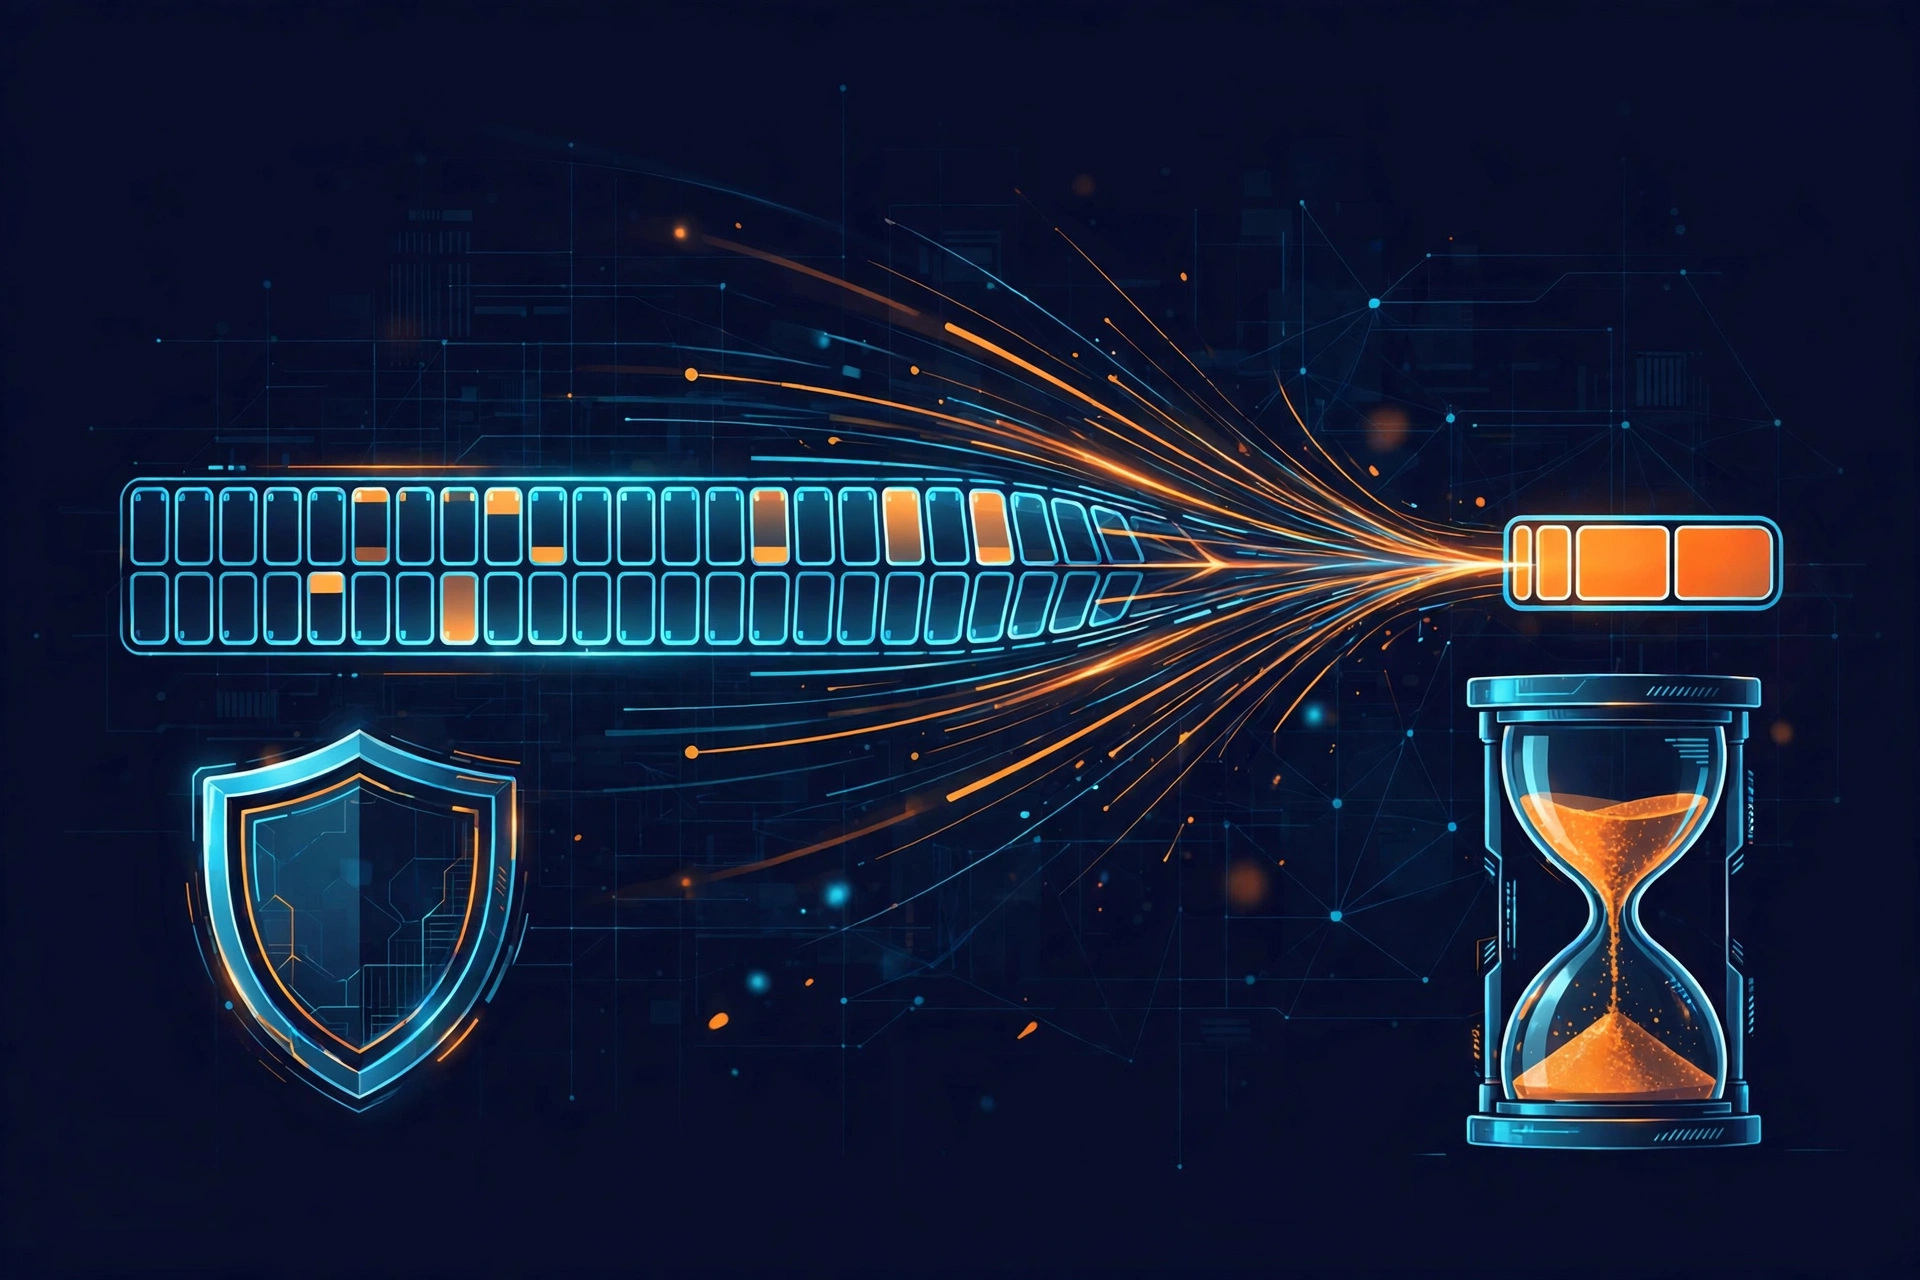
Since 2021, Project Zero followed a “90 + 30” policy. A vendor got up to 90 days to fix a reported vulnerability, plus an extra 30 days of “soak time” for the patch to roll out to users before the details went public. The goal was to encourage faster patching while giving vendors time to deliver fixes.
The new policy, announced in a post titled “Policy and Disclosure: 2026 Edition” by researcher Natalie Silvanovich, replaces that two-stage window with a single fixed clock called “Full X”: a vulnerability is disclosed X days after it is reported to the vendor, whether or not a patch exists.
Source: 30-day disclosure clock.
The phase-in runs on a fixed schedule:
- Full 90 — now: vulnerabilities are disclosed 90 days after they are reported.
- Full 60 — February 2, 2027: the window drops to 60 days.
- Full 30 — January 3, 2028: the window drops to 30 days.
That is a 75 percent cut from the old 120-day ceiling, phased in over about 14 months. Project Zero is also removing most of the policy’s special cases, including the grace period and the variant policy that used to extend deadlines for related bugs.
Why AI forced the change
Project Zero gives three reasons, and all of them trace back to large language models.
First, LLMs have sharply increased the speed at which attackers can find and exploit vulnerabilities — and the risk that several parties, including malicious ones, discover the same bug independently. As the announcement puts it, a vulnerability reported today presents a much higher immediate risk to users than one reported last year.
Second, LLMs have collapsed the time between a patch being released and an attacker reverse-engineering it into a working exploit. Project Zero says near-zero patch-to-exploitation time is now a reasonable model of attacker behavior. That makes the old 30 days of soak time meaningless: once a fix ships, attackers can almost immediately work out the bug details from it, and the extra month of secrecy only creates a false sense of safety.
Third, the sheer volume of reports has exploded. Project Zero says it is now finding several vulnerabilities a week in targets where it once found a few a year. Anything in the policy that requires negotiation with a vendor — such as arguing over whether a bug counts as fixed, or whether a grace period applies — is becoming unmanageable at that volume. A single fixed clock can be automated by both sides; a negotiated one cannot.
What stays the same: the exceptions
The new policy is strict, but it is not absolute. Three exceptions remain:
- Vulnerabilities actively exploited in the wild are handled under Google’s application security vulnerability disclosure policy, which moves faster still.
- Already-public vulnerabilities may be disclosed at Project Zero’s discretion if someone else has already published the details.
- Vendor requests: if the vendor asks for the details to be published, Project Zero will publish them.
Project Zero also says it will continue to grant rare exceptions, as it has done in the past for Spectre and Meltdown, the hardware flaws that needed coordinated, industry-wide fixes. And while the team will still track whether bugs are fixed and tell the public when they are not, fix status will no longer decide the disclosure date. The team acknowledges that deciding whether a bug is truly fixed has always been difficult — especially for code that is not shipped directly to users — and that it is getting harder as vendors experiment with mitigations that are not traditional patches, such as temporarily disabling a vulnerable code path.
Severity, notably, plays no role in the new timeline. Project Zero argues that a bug’s severity changes its impact on users, not the likelihood that attackers will find it, so severity is not an effective metric for disclosure decisions.
Why the phase-in is gradual
If the new timeline is safer, why not switch to 30 days immediately? Project Zero says it asked the vendors it reports the most bugs to, and their feedback shaped the schedule. Vendors warned that an instant switch could harm users by exposing unfixed vulnerabilities while their teams were still improving their patching processes. They also raised two subtler concerns: an overly aggressive policy could push vendors to prioritize newly reported bugs over older, more severe ones, and a deadline some vendors cannot meet might lead them to stop trying altogether.
The phased schedule is the compromise: challenging but realistic, designed to push vendors to improve their remediation processes and infrastructure broadly, rather than to punish any single missed deadline. The team hopes the end result is an industry that can fix all reported vulnerabilities quickly — not just the ones under a Project Zero clock.
What this means for you
For most people, the practical takeaway is simple: install updates faster. The “patch gap” — the time between a fix being released and you installing it — is now the weakest link. Under the old policy, details of a bug stayed secret for up to 30 days after a patch shipped, giving you a cushion. Under Full 30, the details of an unfixed or barely-patched bug could become public a month after the vendor first heard about it. If you have not installed the update by then, you are exposed while the exploit details are in the open.
A few concrete habits matter more than ever:
- Turn on automatic updates for your operating system, browser, and apps, and do not postpone them. On Android and iOS, check that security updates are actually installing — not just downloading.
- Patch promptly when a vendor issues an out-of-band fix. Emergency updates usually mean a flaw is already being exploited or is about to be.
- Do not ignore update prompts on the devices you forget about — routers, smart TVs, cameras, and old phones are exactly the devices that stay unpatched the longest.
For IT teams and developers, the message is blunter: build your patching pipeline as if a 30-day public deadline is already here, because in just over a year it will be. Vendors that still treat security fixes as quarterly events will find themselves racing a clock they cannot negotiate with.
The bigger picture: disclosure norms are shifting
Project Zero’s move does not happen in isolation. November has already shown how fast serious flaws are moving: the same week as the announcement, a critical Apache HTTP Server flaw forced an emergency patch to version 2.4.71, a reminder that the window between a bug being known and being exploited is shrinking across the whole industry.
See also: exploited vulnerabilities.
Project Zero’s policy has long served as a benchmark that other researchers and vendors measure themselves against. If its 30-day clock becomes the norm, expect other bug-hunting teams and bug bounty programs to tighten their own timelines — and expect vendors to invest more in automated patching, faster rollouts, and non-patch mitigations that protect users while a full fix is still being built.
The old bargain was that secrecy bought safety: keep a bug quiet for a while and users stay protected. AI has broken that bargain. Attackers can now find bugs faster, reverse-engineer patches in hours, and rediscover the same flaws independently. Project Zero’s answer is to stop pretending the secret lasts, and instead make the fix arrive faster. For users, the best response is the simplest one: keep your software updated, and stop treating the update button as optional.
Frequently asked questions
What is Google Project Zero?
Project Zero is Google’s team of security researchers who find serious vulnerabilities in software made by other companies — including Microsoft, Apple, and open-source projects — and report them to the vendor before publishing the details publicly.
When does the 30-day disclosure deadline take effect?
The new policy starts at Full 90 (disclosure 90 days after reporting). It moves to Full 60 on February 2, 2027, and to Full 30 on January 3, 2028.
Does Project Zero publish bugs even if the vendor has not fixed them?
Yes. Under the new “Full X” policy, disclosure happens a fixed number of days after the report, regardless of whether a patch exists. Project Zero will still say whether a bug is fixed when it publishes.
Are there any exceptions?
Yes. Bugs already being exploited in the wild follow a separate, faster policy; bugs whose details are already public may be disclosed sooner; and a vendor can ask for earlier publication. Rare exceptions, as with Spectre and Meltdown, remain possible.
What should I do differently as a user?
Install security updates as soon as they appear, enable automatic updates everywhere you can, and pay attention to emergency patches — the cushion between a fix shipping and its details going public is disappearing.
Related reading: cybersecurity threats to watch in 2026.