Two weeks after a malicious copy of Anthropic’s Claude Code extension appeared in its marketplace, Cursor has published the full story of how it happened — and the trail leads back to a single access key at one of its AI vendors.
In an incident update published on November 13, 2026, Cursor says the attack began at Fireworks AI, an inference vendor it used for model training and inference. An access key Cursor had issued to Fireworks was exposed by Fireworks, and an attacker used it to copy data from a shared storage bucket. From there, the attacker worked through stolen credentials, reached Cursor’s internal tools, and eventually planted the tampered extension where thousands of developers could download it.
It is a textbook supply-chain attack — except the compromised link was not a package or a library. It was a vendor relationship. Anthropic, the maker of Claude Code, is itself in the spotlight as its IPO filing heads toward a November 19 Nasdaq debut.
How the Attack Unfolded
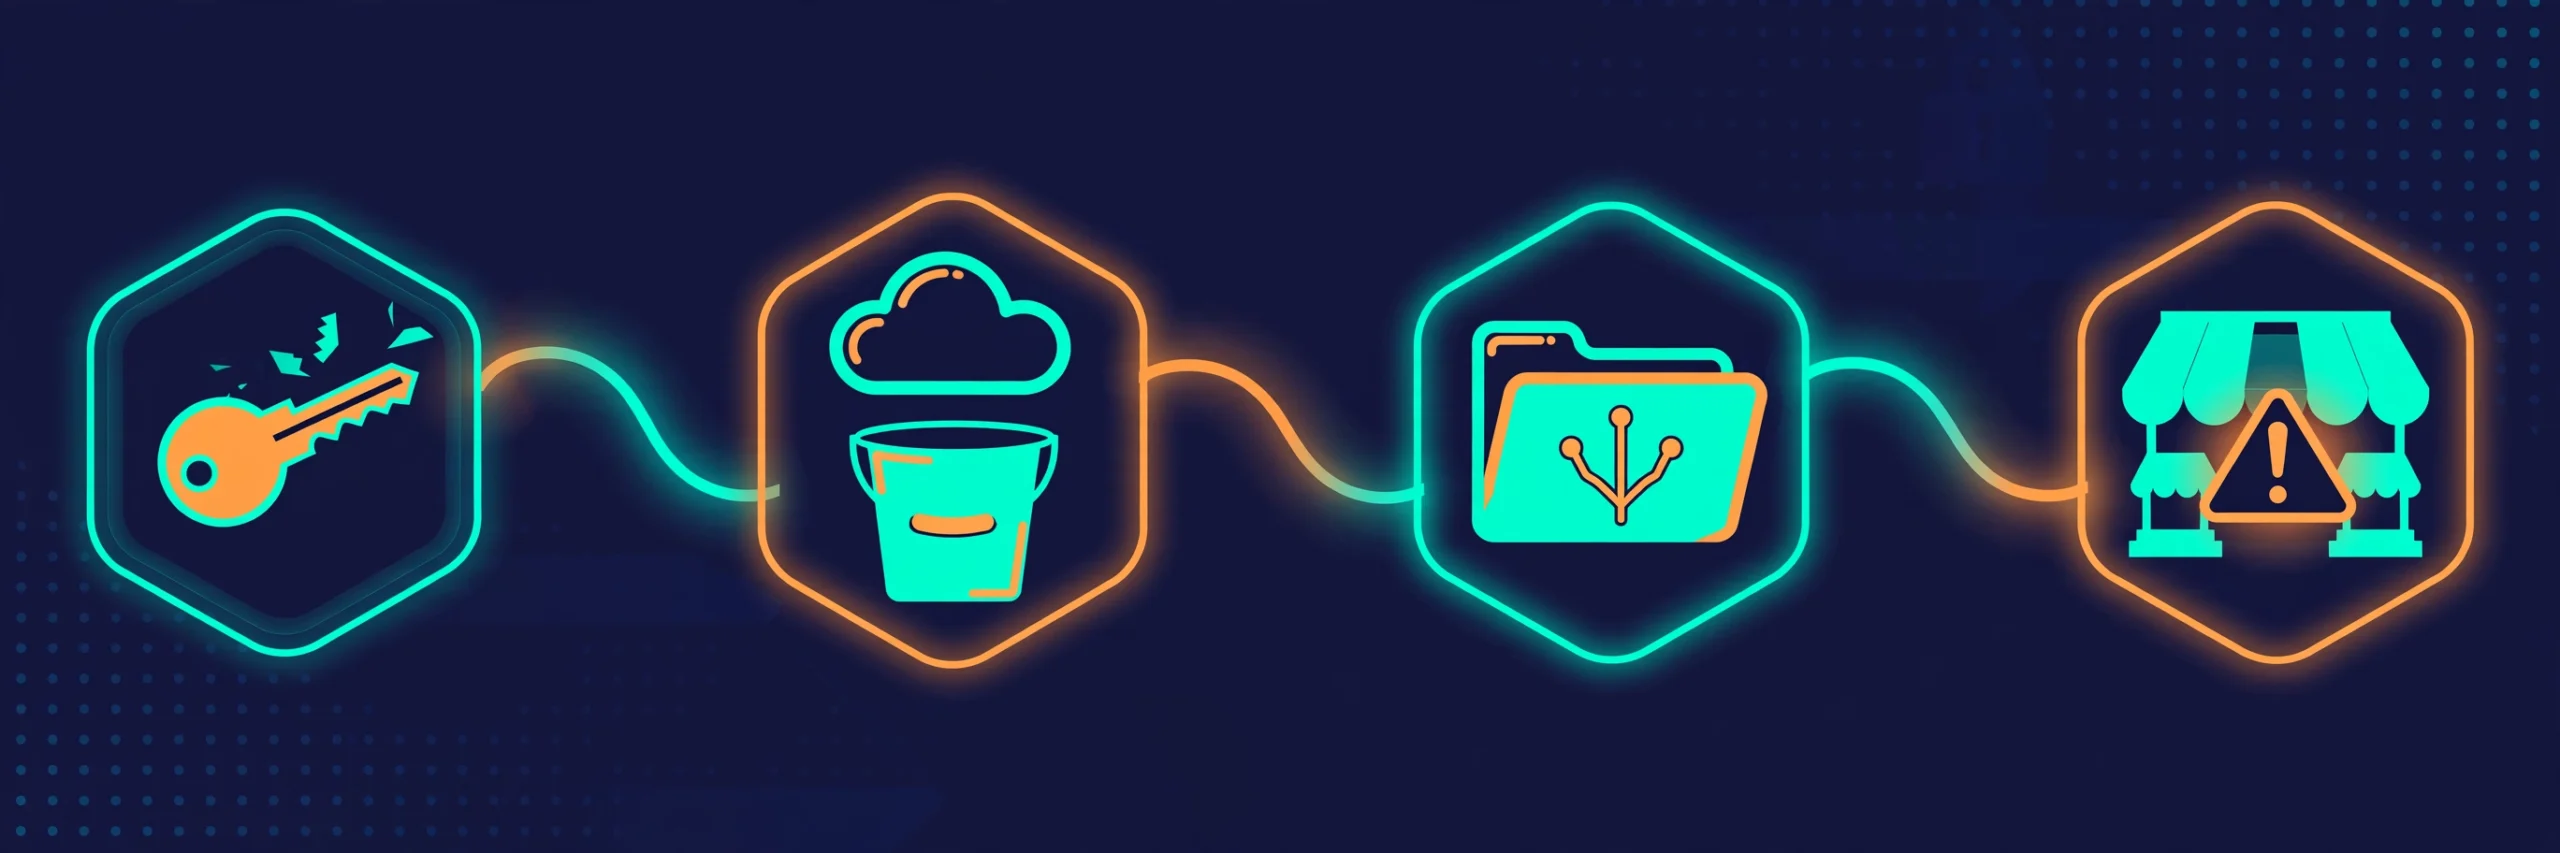
Cursor’s investigation reconstructs the incident in five stages, and each one shows how a small exposure can cascade.
It started at Fireworks. The attacker obtained a Cursor-issued access key that Fireworks had exposed, then used it to copy data from a read-only storage bucket the two companies used to share data. The bucket held limited coding agent traces — mostly from 2025, from sessions that were not in Privacy Mode and that Cursor was permitted to use for model training. A small number of those traces contained credentials that had not been redacted. Fewer than 0.01% of customers had API credentials exposed, Cursor says.
The attacker moved laterally. Starting with those credentials, the attacker reached select software-as-a-service tools Cursor used, and from them accessed archived non-production source code repositories, limited customer support data and email conversations, product usage metrics and contact details, summaries of some coding agent conversations, and credentials some users had sent to Cursor’s support team.
The malicious extension was planted. On October 29, using a stolen credential from the exposed internal data, the attacker placed malicious, unauthorized copies of Anthropic’s Claude Code extension — versions 2.1.312 and 2.1.313 — directly on the cache that serves the Cursor VS Code extension marketplace. Anthropic did not publish these copies, Cursor stresses, and the incident was not a vulnerability in Anthropic’s product. The marketplace source, Open VSX, never hosted the malware. At most 5,000 users who requested those specific cached versions potentially received the malicious build, which was available for approximately 11 hours before Cursor removed it.
Customers were notified. On October 30, Cursor published a security notice with indicators of compromise, remediation steps and scripts to check affected machines, and began notifying users and team admins through in-app notices and email. Team admins whose credentials were exposed received a list of the specific keys to rotate, and Cursor asked the third-party services that issued those credentials to revoke them.
The incident is contained, Cursor believes. The last attacker activity the company has seen was on November 1, and it was blocked. Monitoring continues.
What Was Exposed — and What Was Not
The numbers are small, but the data involved is sensitive. Coding agent traces were exposed for fewer than 0.05% of users who were not using Privacy Mode, and Cursor says it has identified and contacted each of them directly. If you did not receive a notification, your data was not in those traces, according to the company.
Just as important is what Cursor says the attacker did not touch: prompts and code from Privacy Mode users, any data or live traffic being sent to Cursor right now, the production systems that run the service, the Cursor app and its official updates, release signing keys, customer code repositories, and any other extension in the marketplace. The company says it validated every other extension as authentic and rebuilt the marketplace store. Anthropic has also been shipping fast: Claude Fable 5.2 and Mythos 5.2 arrived this week with faster, cheaper frontier models.
The Fireworks Side of the Story
Fireworks AI disclosed its own October incidents separately. In a November 9 update, the company said a second intrusion had reached its systems through a third-party cloud provider that hosted its research and development machines — an incident on October 23, with the attacker reaching Fireworks development machines the next day. Billing records were exposed, and for a limited set of accounts, secrets, datasets and incomplete model weights were also reached. Fireworks says it has not detected further successful unauthorized access on its customer platform since October 25, and it is working with Palo Alto Networks Unit 42 on the investigation.
Notably, Fireworks’ own bulletins do not mention Cursor — the connection between the two incidents comes from Cursor’s account. That gap is worth remembering: when a breach spans two companies, each side’s disclosure may tell only its own half of the story.
What Cursor Has Done Since
Cursor’s remediation list is extensive, and it reads like a checklist every company should have ready before an incident, not after one:
- Moved all inference traffic off Fireworks, deactivated the key it had issued to the vendor, and cut off Fireworks’ access to all shared datasets.
- Rotated every exposed credential, highest risk first, and as a precaution rotated all credentials in use across its internal systems — even where there was no evidence of exposure.
- Expanded network access restrictions across service providers so compromised credentials cannot be used outside their intended location.
- Added secret scanning and protections across all code repositories, and expanded scanning to other internal data sources.
- Redeployed all production infrastructure and services as a precaution, reviewing every internal service before restoring it.
- Engaged external forensics experts to support the investigation.
What Developers Should Do Now
If you installed or updated Anthropic.claude-code versions 2.1.312 or 2.1.313 from the Cursor VS Code extension marketplace on October 29, follow the steps in Cursor’s security notice — and note that uninstalling the extension alone may not be enough — see our earlier coverage of the fake Claude Code extension, which explains how to check your machine for the SSH backdoor the tampered build planted.
More broadly, the incident is a reminder that the tools developers trust most — their editors, their extensions, their AI coding assistants — are only as secure as the weakest vendor in the chain. A leaked key at a supplier became a backdoored extension in a marketplace used by millions. The fix is not just better key hygiene, though that matters. It is treating every third-party integration as a potential entry point, with scoped credentials, short lifetimes, and monitoring that catches misuse early. As AI agents take on more trusted work — even handling payments on users’ behalf — the security of the tools around them matters more than ever.
Cursor apologized to those affected and said it “can and must do better.” For developers, the lesson is simpler: check your extensions, rotate exposed keys, and never assume the marketplace did the checking for you.
Sources: Cursor’s incident update (https://cursor.com/blog/security-incident-update), Unite.AI (https://www.unite.ai/cursor-traces-breach-to-access-key-exposed-by-fireworks-ai/), Cyber Security News (https://cybersecuritynews.com/cursor-data-breach/).